


We used to fear the people who watched us from outside our homes. Today, we willingly carry the watcher in our pockets.
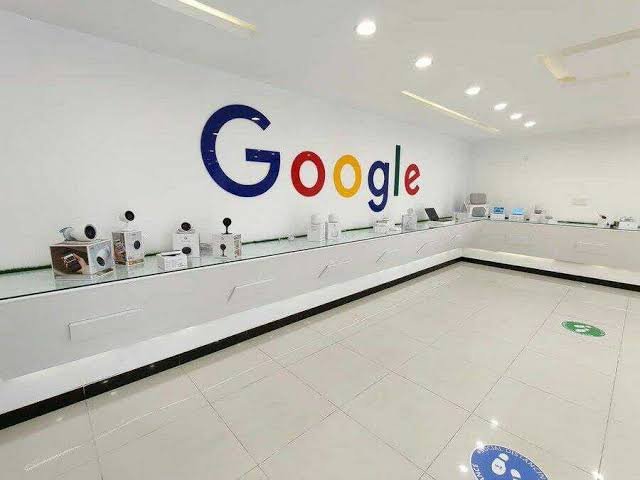
Google has opened its first local office in Pakistan, which has been termed as a landmark achievement for the digital economy of the country. However, with all the excitement that has ensued over this development, there remains one critical question that cannot be overlooked: with Google moving closer to Pakistan, who will safeguard the data of Pakistanis?
There is no doubt that Google has long been entrenched in our lives. We seek information about health issues, navigate the world with Maps, correspond via Gmail, watch YouTube, and use Android devices that track our location. Google’s Privacy Policy states that it collects information about searches, locations, devices, and users’ interactions with its products. But privacy settings are not the same as legal rights.
This is where Pakistan’s enthusiasm collides with its legal gap. Google continues to establish its presence in a country that still lacks effective legislation to protect personal data.
Article 14 of the Constitution of Pakistan provides that the dignity of man and the right to privacy of his home are secured subject to law. And the courts in Pakistan have also acknowledged the possibility that this right to privacy includes information kept by individuals on their devices. But the question for Pakistan today is broader: when companies collect our searches, locations, communications and other personal information as part of ordinary digital life, what law governs that collection and use?
The issue of Pakistan is not that it is devoid of digital laws. It is that those laws do not form one unified data-protection framework.
One such example is “The Prevention of Electronic Crimes Act, 2016.” It is a significant instrument in Pakistan’s digital framework, covering offences related to unauthorised access, interference, electronic fraud, and other cybercrimes. The 2025 amendment to this further reshaped the regulatory landscape of online activities. But PECA is primarily a criminal law. It covers instances where such behaviour becomes criminal, but it does not provide an exhaustive list of rights regarding how organisations can handle people’s private data.
A person should not have to wait until their data is stolen or unlawfully accessed for the law to become relevant. Data protection starts earlier with rules about what can be collected, why it should be collected, and what happens to it afterwards.
The problem, however, is not new. Pakistan has been attempting to fill this gap for years. The Personal Data Protection Bill, 2023 proposed a dedicated framework for personal data and to establish a National Commission for Personal Data Protection. The Senate record, however, indicates that the Bill was not passed or rejected by the appropriate committee.
More recently, Pakistan has taken steps to enhance data governance with the National Data Governance Policy 2026, which has moved from draft to finalisation. That is a positive step, but a governance policy cannot substitute for comprehensive legislation that protects personal data throughout its entire lifecycle.
So, it’s not wrong to say that Pakistan knows that the gap exists. It has simply chosen not to close it.
The problem becomes more prominent when the data doesn’t stay in Pakistan. Google says it processes data on servers outside the user’s country. This poses a pertinent issue for the people of Pakistan regarding who will have the right to investigate whether any misuse has been committed with this data and what recourse is available to the concerned person.
The company’s privacy policy cannot address all issues related to jurisdiction. Moreover, it is not fair that the security of the personal information of Pakistanis would be dependent upon the terms and conditions of a foreign company. This gap should be filled by enacting a comprehensive framework that lists down the rules and remedies for Google and people of Pakistan.
This is not merely a theoretical concern. In May 2025, the National Cyber Emergency Response Team (PK-CERT) of Pakistan warned of a data breach of login credentials and passwords of over 180 million Internet users. The reported data contained usernames, passwords, email addresses, and URLs for big tech companies, government sites, banks and health care providers. The breach was carried out using infostealer malware capable of extracting sensitive data from infected devices.
Such stolen credentials can lead to account takeovers, identity theft, phishing and further unauthorised access. Citizens cannot be expected to carry the entire burden of protecting data collected and processed at an enormous scale.
Pakistan tends to formulate regulations only after the harm has been done. Data protection cannot follow the same trajectory. We require a preventive model in which organisations collect only what is necessary, inform citizens about how their data will be processed, and outline the measures taken in the event of a breach. Individuals have the right to know how their data has been collected and processed and who has access to it.
The entry of Google into Pakistan should not just mark an important phase in Pakistan’s digital age. It must remind us that we have brought big data organisations into our jurisdiction without knowing the legislation which will ensure the rights of the people whose data will build the digital economy.